Fort Firewall v3.20.2 Adds Kernel Enforcement and Per-Rule Scheduling
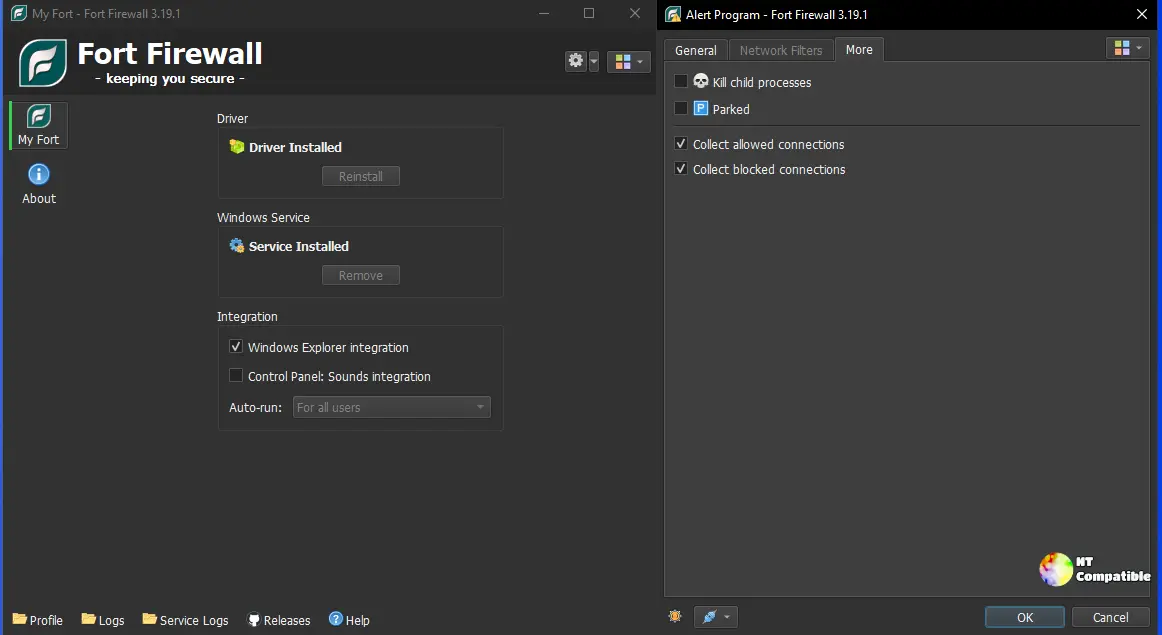
Fort Firewall has shipped version 3.20.2 today, landing the third update in just four days for its rapidly expanding v3.20.x series. The build pushes per-program Network Filters down to the kernel driver for tighter enforcement and finally allows Time Periods on individual rules, letting you schedule traffic blocks directly without juggling separate groups. It builds on the massive feature wave from early October that introduced a Filter Simulator, per-app speed limits, and a streamlined connection log that tracks inherited process access. Available for Windows 7 through 11 on x86, x86_64, and ARM64 architectures, the update requires disabling Memory Integrity on newer builds but keeps its reputation as a lean, open-source alternative to bloated security suites.
Fort Firewall v3.20.2 Adds Kernel Enforcement and Per-Rule Scheduling @ NT Compatible
Fort Firewall v3.20.2 Adds Kernel Enforcement and Per-Rule Scheduling
Fort Firewall has released version 3.20.2, introducing kernel-level enforcement for per-program Network Filters and the ability to schedule time periods for individual rules. This update is part of a rapid expansion of the v3.20.x series that includes significant features like a Filter Simulator and per-app speed limits. The new architecture enhances security by ensuring that network filter rules are evaluated at the kernel level rather than userspace, closing potential bypass vulnerabilities. Despite some limitations, such as the need to disable Memory Integrity on Windows 10 and 11, the update solidifies Fort Firewall's reputation as a lean, open-source alternative to more bloated security solutions