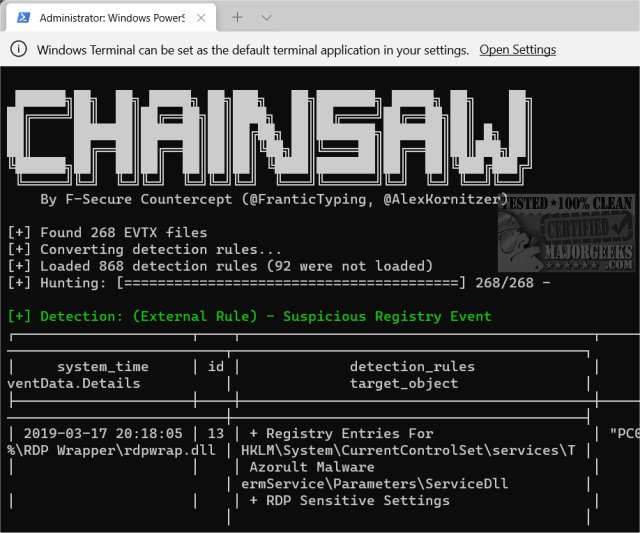
Chainsaw version 2.17.1 has been released, enhancing the ability for advanced users to efficiently search and analyze Windows Event Logs. This tool is designed to facilitate rapid threat identification within event logs, providing a robust 'first-response' capability. With its powerful search functions, Chainsaw enables users to extract event log records based on event IDs, string matches, and regex patterns. It also supports Sigma detection rules, allowing for customized threat hunting using built-in detection logic.
Key features of Chainsaw include:
- High-speed performance, thanks to its Rust programming, which integrates the EVTX parser library by OBenamram.
- Document tagging through the TAU Engine Library, which helps in matching detection logic.
- Flexible output options, including ASCII table format, CSV, and JSON.
Chainsaw is tailored for advanced users familiar with Command Prompt, making it particularly beneficial for technicians, administrators, and IT professionals. For those interested in trying out the program, a sample command can be executed from the folder where the files are extracted: `./chainsaw hunt evtx_attack_samples/ --rules sigma_rules/ --mapping mapping_files/sigma-mapping.yml`.
To further assist users, additional resources are available, such as guides on clearing all event logs in Windows Event Viewer and understanding how to read Event Viewer logs for Check Disk operations. This makes Chainsaw not only a powerful tool for log analysis but also part of a broader toolkit for IT professionals seeking to enhance their system security measures.
In summary, Chainsaw is a vital resource for threat detection and analysis within Windows environments, providing advanced capabilities for those who need to quickly respond to potential security incidents
Chainsaw 2.17.1 released
Chainsaw allows advanced users to search and hunt through Windows Event Logs rapidly.