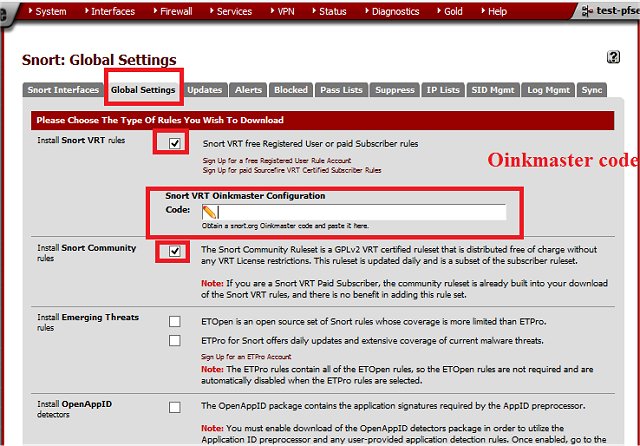
Snort 3.13.2.0 has been released, showcasing its capabilities as an Open Source network intrusion prevention system (IPS) that conducts real-time traffic analysis and packet logging on IP networks. Contrary to the notion that network security is solely in the domain of IT professionals or large corporations, Snort provides an accessible option for even casual users aiming to secure their networks.
To clarify its role, Snort is not a firewall, which primarily serves to filter incoming and outgoing traffic based on defined rules. Instead, Snort operates as an Intrusion Detection System (IDS) and IPS, focusing on detailed analysis of network traffic to identify potential threats such as malware and suspicious activity. When configured as an IPS, Snort can actively take measures such as dropping malicious packets, but its core strength lies in threat detection and detailed logging for further analysis.
Snort's versatility is enhanced by a robust, constantly updated rule-based detection system supported by both the Snort community and Cisco, ensuring users remain ahead of evolving threats. Additionally, it is scalable, accommodating networks of any size, from small setups to expansive infrastructures.
Getting started with Snort involves using the Command Line, which may present challenges for new users. However, it is advised to familiarize oneself with the installation files and the basic commands. Snort operates in various modes—Sniffer Mode for real-time traffic capture, Packet Logger Mode for data recording, and Network Intrusion Detection Mode for detecting and blocking suspicious traffic.
In summary, Snort acts as a vigilant watchdog for network security, offering enterprise-level protection at no cost. While it may have a learning curve, leveraging community resources and tutorials can facilitate the learning process. Users are encouraged to start with Snort in "sniffer" mode to get accustomed to its functionalities and to maintain backups of configurations before making changes. Additionally, users experiencing issues should consider installing WinPCAP and updating their Microsoft Visual C++ Redistributable Package for optimal performance.
As network security continues to be a critical focus for organizations of all sizes, tools like Snort empower users to take control of their network defenses. By providing robust, customizable, and scalable solutions, Snort not only enhances security but also fosters a community of users dedicated to improving network safety protocols
To clarify its role, Snort is not a firewall, which primarily serves to filter incoming and outgoing traffic based on defined rules. Instead, Snort operates as an Intrusion Detection System (IDS) and IPS, focusing on detailed analysis of network traffic to identify potential threats such as malware and suspicious activity. When configured as an IPS, Snort can actively take measures such as dropping malicious packets, but its core strength lies in threat detection and detailed logging for further analysis.
Snort's versatility is enhanced by a robust, constantly updated rule-based detection system supported by both the Snort community and Cisco, ensuring users remain ahead of evolving threats. Additionally, it is scalable, accommodating networks of any size, from small setups to expansive infrastructures.
Getting started with Snort involves using the Command Line, which may present challenges for new users. However, it is advised to familiarize oneself with the installation files and the basic commands. Snort operates in various modes—Sniffer Mode for real-time traffic capture, Packet Logger Mode for data recording, and Network Intrusion Detection Mode for detecting and blocking suspicious traffic.
In summary, Snort acts as a vigilant watchdog for network security, offering enterprise-level protection at no cost. While it may have a learning curve, leveraging community resources and tutorials can facilitate the learning process. Users are encouraged to start with Snort in "sniffer" mode to get accustomed to its functionalities and to maintain backups of configurations before making changes. Additionally, users experiencing issues should consider installing WinPCAP and updating their Microsoft Visual C++ Redistributable Package for optimal performance.
As network security continues to be a critical focus for organizations of all sizes, tools like Snort empower users to take control of their network defenses. By providing robust, customizable, and scalable solutions, Snort not only enhances security but also fosters a community of users dedicated to improving network safety protocols
Snort 3.13.2.0 released
Snort is an Open Source network intrusion prevention system capable of performing real-time traffic analysis and packet logging on IP networks.