An emergency patch has been released for critical remote code execution vulnerabilities in PHP, known as PHP2Shell, with a CVSS rating of 9.2, and Sury.org has made updates available for all PHP versions from 5.6 to 8.5 on Debian and Ubuntu. The patch is applied natively for four supported branches, while the seven end-of-life branches also receive backported protections. This update allows operators using older PHP versions to secure their systems without needing to upgrade to a newer version, which is a significant relief for those still reliant on legacy installations. The vulnerabilities can lead to memory disclosure and unauthorized access, making it crucial for organizations to update promptly, as no complete mitigations other than updating are available
PHP2Shell Patch: Sury.org Ships Debian Ubuntu Updates for Every PHP Version from 5.6 to 8.5
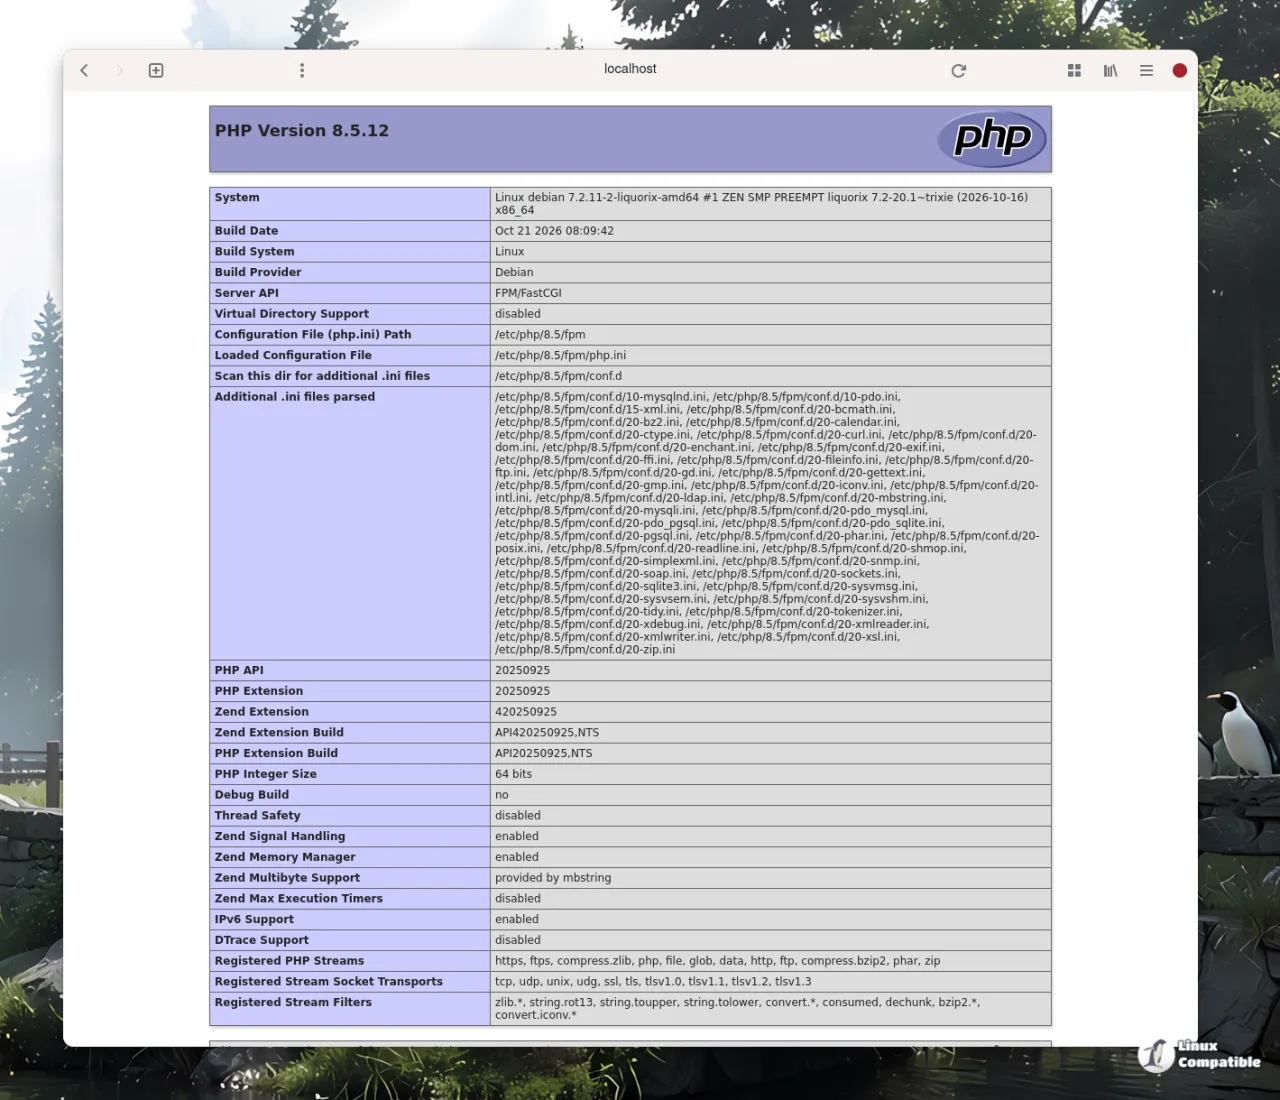
PHP issued an emergency out-of-band patch today for two critical RCE flaws dubbed PHP2Shell, rated 9.2 on CVSS v4.0, and sury.org has already published the builds for Debian and Ubuntu. The four current branches get native fixes, 8.5.12, 8.4.27, 8.3.36, and 8.2.35, while the seven end-of-life branches from 8.1 down to 5.6 get the same protection backported. Since the bugs permit unauthenticated RCE and memory disclosure across every deployment model, PHP says updating is the only reliable fix, though interim steps like disabling session.upload_progress can buy a little time. Operators can update in place with a standard apt command and then restart PHP-FPM or Apache, sidestepping the emergency migration many had feared.