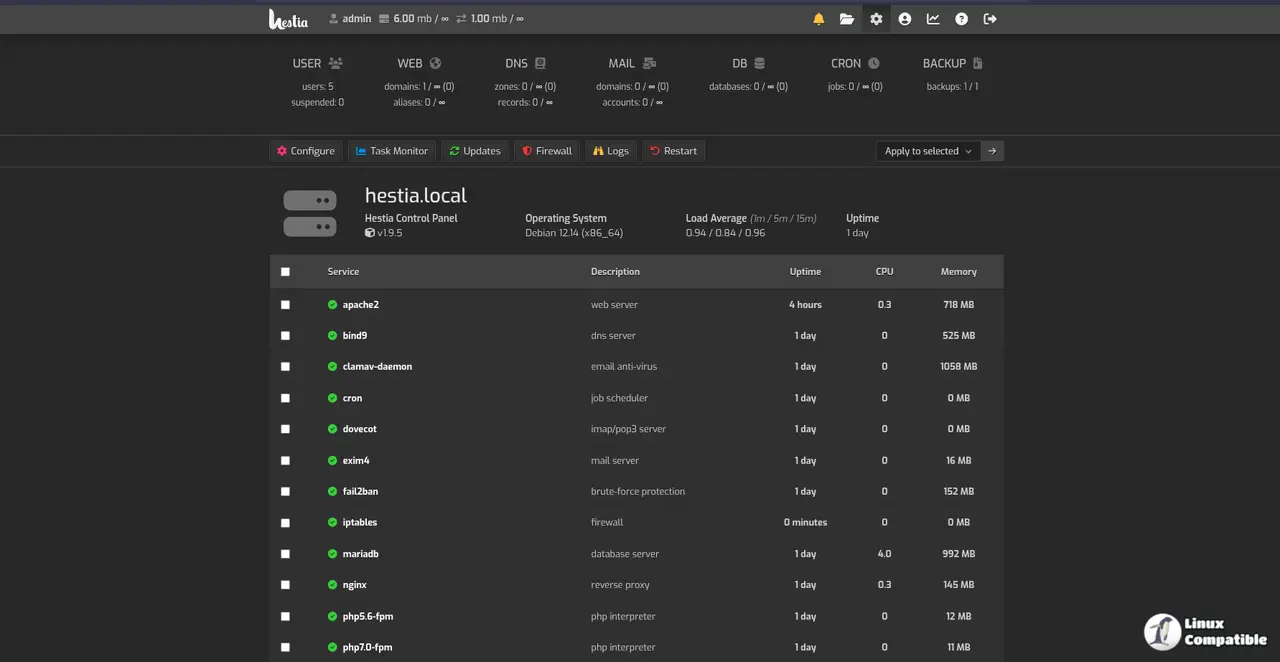
Hestia Control Panel has released version 1.10.8, focusing on security improvements including three major fixes to enhance two-factor authentication (2FA), prevent open redirects, and restrict backup downloads to individual users. The update also addresses CSRF issues, revives a previously inactive Fail2Ban jail, and updates key dependencies like Nginx and SnappyMail. This release continues a year-long effort to strengthen the platform's security, with maintainers urging users to upgrade promptly to benefit from these critical fixes. The consistent updates reflect a commitment to closing vulnerabilities and enhancing the integrity of a control panel that manages essential web services
HestiaCP 1.10.8 Release: 3 Security Fixes, 2FA Hardening and Dependency Updates
Hestia Control Panel released version 1.10.8 today as a security-focused service release led by maintainer Jaap Marcus. The update's three headline fixes stop 2FA QR codes from leaking auth secrets to a third-party API, block post-login open redirects, and prevent users from downloading other accounts' backup archives. It also patches CSRF issues on reset pages, revives an inert Fail2Ban jail, and bumps key dependencies like Nginx to 1.30.7 and SnappyMail to 3.1.3. Given that these changes build on a year-long hardening campaign, the maintainers recommend upgrading immediately.
HestiaCP 1.10.8 Release: 3 Security Fixes, 2FA Hardening and Dependency Updates @ Linux Compatible