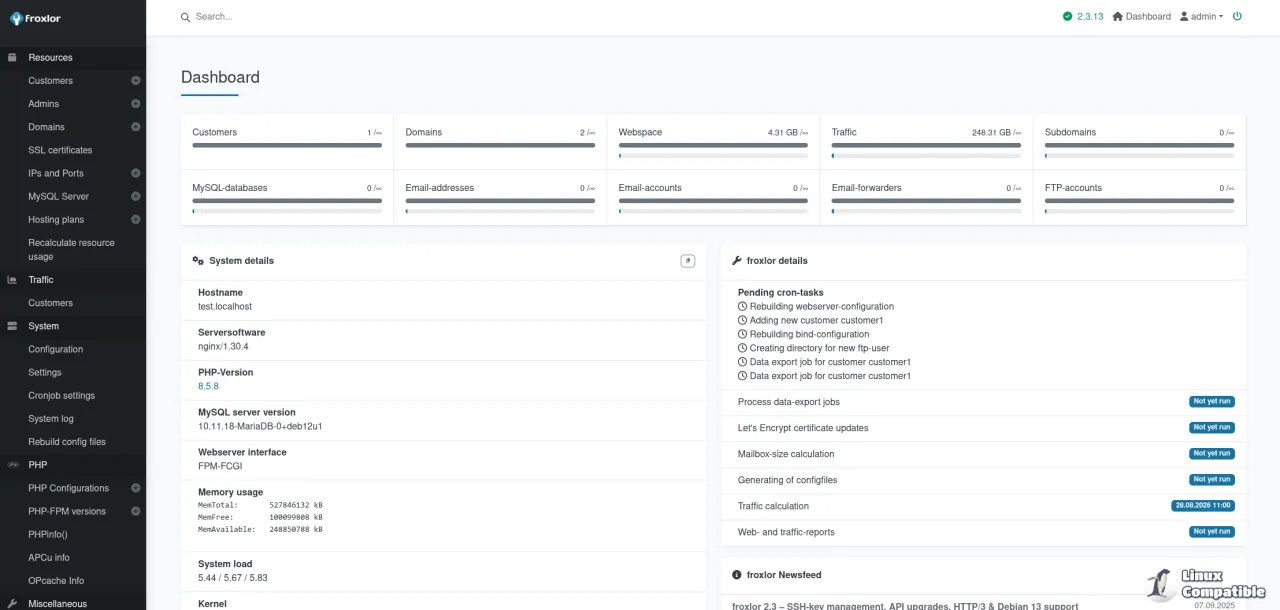
Froxlor has released version 2.3.14 as a security update, addressing four key vulnerabilities alongside two regular bug fixes. The updates include enhanced authorization controls on server-wide reads, validation against installed themes to mitigate XSS risks, rejection of control characters to prevent FTP injection, and restrictions on mail-body access between admins. This release is part of a broader effort to harden the software, which has seen similar security improvements in prior versions. Operators are encouraged to update promptly due to session invalidation and the need for API key rotation that accompanies at least one of the fixes
Froxlor 2.3.14 Security Release: Four Fixes, Now Available
Floxlor released 2.3.14 today as a full security update, with all four changes tagged [Security] in the changelog. Maintainer Michael Kaufmann (d00p) shipped it as the newest entry in a coordinated hardening sweep across the 2.3.x branch, following similar fixes in 2.3.10, 2.3.11, and 2.3.13. The patches close authorization gaps on server-wide reads, an XSS theme vector, CRLF/FTP injection, and cross-admin mail exposure, alongside two regular bug-fixes. Operators should update sooner rather than later, since at least one fix invalidates active sessions and pushes API-key rotation.
Froxlor 2.3.14 Security Release: Four Fixes, Now Available @ Linux Compatible