Snort 3.12.4.0 has been released, marking an important update for this Open Source network intrusion detection and prevention system (IDS/IPS). Unlike traditional firewalls, which act as barriers to filter network traffic based on preset rules, Snort provides a deeper analysis of network traffic. It is designed to detect potential threats, such as malware and suspicious behavior, by comparing incoming data against a set of predefined rules. If configured as an IPS, Snort can take proactive measures, like dropping malicious packets, but its primary function is to identify threats and generate detailed logs for further analysis.
Snort's versatility is one of its strongest features. With a robust, rule-based detection system that is continuously updated by both the Snort community and Cisco, users can stay ahead of evolving cyber threats. It is scalable, catering to both small networks and larger, growing infrastructures.
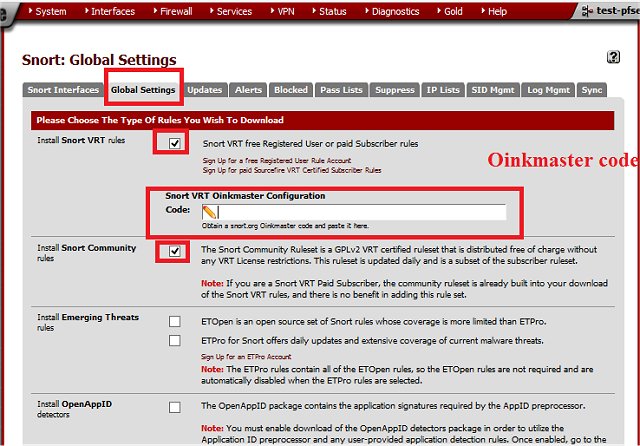
Getting started with Snort requires familiarity with command-line interfaces, as it primarily operates through a Command Line application. Although GUI options exist, they may not be as straightforward to set up. New users should begin by reading the documentation found in the installation folder and trying basic commands to familiarize themselves with the system. Snort includes built-in rules for common threats and allows users to download community-created rules or develop their own custom rules for specific monitoring needs.
Snort operates in multiple modes, including Sniffer Mode for real-time traffic capture, Packet Logger Mode for later analysis, and Network Intrusion Detection Mode for comprehensive threat detection and prevention.
In summary, Snort offers enterprise-level network protection for free, making it accessible for users ranging from casual to professional. To maximize its effectiveness, beginners should start with the Sniffer Mode, utilize community resources for guidance, and ensure they back up configuration files before making significant changes. For troubleshooting, installing WinPCAP and updating the Microsoft Visual C++ 2015-2022 Redistributable Package can resolve common issues.
As the landscape of network security continues to evolve, using tools like Snort not only enhances your security posture but also empowers users to take charge of their network defenses regardless of their technical expertise. With ongoing contributions from the community and advancements in technology, Snort remains a vital resource for anyone looking to bolster their network security effectively
Snort 3.12.4.0 released
Snort is an Open Source network intrusion prevention system capable of performing real-time traffic analysis and packet logging on IP networks.