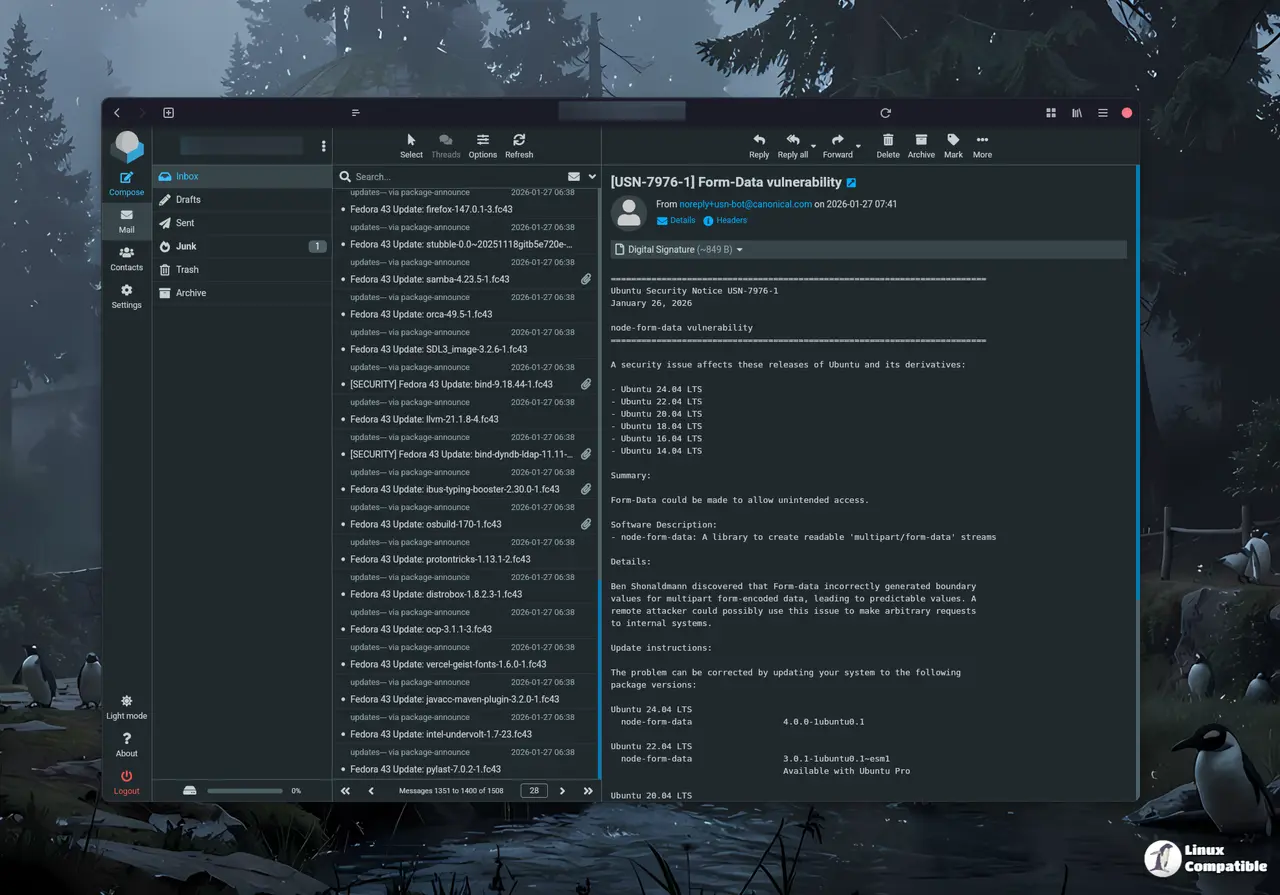
Roundcube has released two critical security updates, version 1.6.20 for its long-term support (LTS) line and version 1.7.5 for the mainline, both addressing 20 recently reported vulnerabilities. The lead developer, Aleksander Machniak, strongly recommends that all users update their installations due to issues related to email-sanitization bypasses, IMAP and header injections, and various other security flaws. Despite Roundcube's widespread use as a backend for many webmail services, it often goes unnoticed, leading to a significant potential impact from any vulnerabilities. The updates are essential for maintaining security and are expected to be assigned CVE numbers soon, so users are advised to back up their data before upgrading
Roundcube 1.6.20 and 1.7.5 Ship 20 Security Fixes
Roundcube released two security updates today, version 1.6.20 for its LTS line and 1.7.5 for mainline, only a minute apart, each fixing 20 recently reported vulnerabilities. Both went out from lead developer Aleksander Machniak, who strongly recommends updating every production installation. The fixes center on email-sanitization bypasses, IMAP and header injection, SSRF, ImageMagick limits, session injection, CSRF and XSS, with a single collective (Squirt1e, Atum, N0b0dy, Gh0u1L5) credited on 8 of the 20. Roundcube says no CVEs are assigned yet but expects them soon, and urges admins to back up first then move to 1.6.20 on LTS or 1.7.5 on mainline.
Roundcube 1.6.20 and 1.7.5 Ship 20 Security Fixes @ Linux Compatible