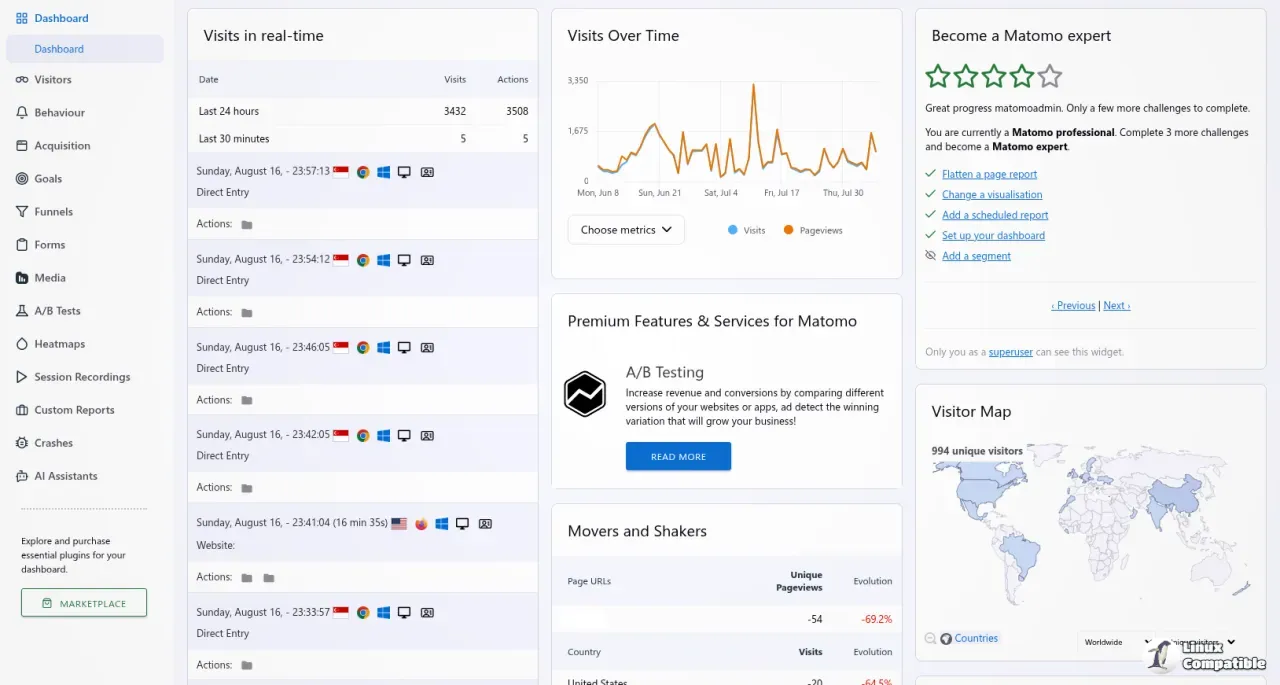
Matomo has released version 5.14.2 in response to two critical PHP vulnerabilities known as "php2shell," which are actively being exploited. The update addresses two issues: a warning mechanism for vulnerable PHP versions within the Matomo UI and an update to the certificate dependency for security. However, the release emphasizes that simply updating Matomo will not fix the vulnerabilities, as the underlying PHP installation must also be patched for true protection. Self-hosted users are urged to check their PHP versions and apply the necessary updates, as the security of their Matomo installations relies on the PHP runtime it operates on
Matomo 5.14.2 Released: Vulnerable PHP Check and Certificate Hardening
Matomo 5.14.2 is core release shipped today, in response to two critical, actively exploited PHP vulnerabilities collectively nicknamed "php2shell." The release closed just two tickets, one flagging vulnerable PHP inside the Matomo UI and another hardening a certificate dependency.
Matomo 5.14.2 Released: Vulnerable PHP Check and Certificate Hardening @ Linux Compatible