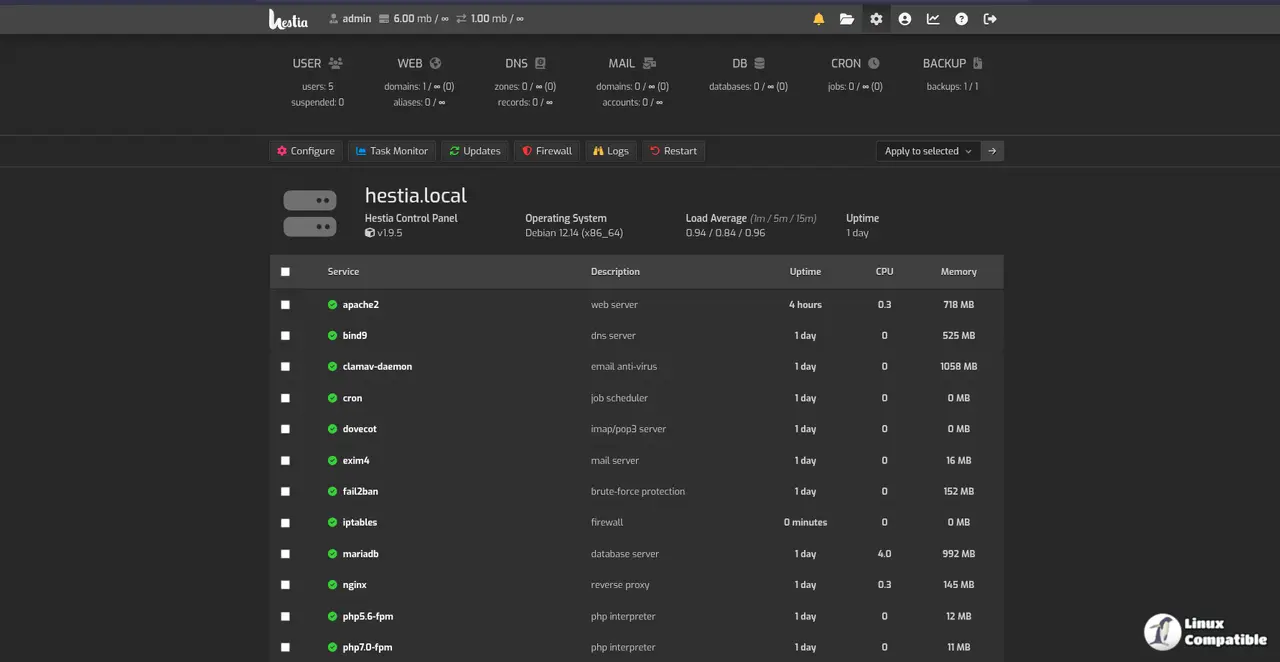
HestiaCP has released version 1.10.7, primarily focused on security fixes that address privilege-escalation and command-injection vulnerabilities. The update includes a significant fix that prevents symlink attacks and enhances input validation across its shell scripts, which are executed with root privileges. Additionally, the release updates several dependencies, introduces minor features like a password-visibility toggle, and improves the overall functionality of the panel. Users are strongly encouraged to upgrade their public-facing servers due to the critical nature of the vulnerabilities addressed in this release
HestiaCP 1.10.7 Security Release Closes Root-Escalation Flaws
HestiaCP released version 1.10.7 today, a service release built mostly around security fixes that plug privilege-escalation and command-injection paths letting low-privilege users grab root. The most consequential fix stops symlink attacks by root and stages restores in root-only directories, addressing flaws first disclosed in a Nov. 8 batch of advisories. It also updates Roundcube, SnappyMail, MariaDB, and Zlib, adds a password-visibility toggle and .xz archive support, and bumps the panel's PHP-FPM pool. Automatic updates are on by default, existing boxes upgrade via apt, and Hestia strongly recommends patching any public-facing server.
HestiaCP 1.10.7 Security Release Closes Root-Escalation Flaws @ Linux Compatible